The visibility layer
'%20stroke-width='1'%3e%3cpath%20d='M%20170.0%20104.0%20L%2092.1%20149.0'%3e%3c/path%3e%3cpath%20d='M%20170.0%20104.0%20L%20247.9%20149.0'%3e%3c/path%3e%3cpath%20d='M%20183.0%20111.5%20L%20105.0%20156.5'%3e%3c/path%3e%3cpath%20d='M%20157.0%20111.5%20L%20234.9%20156.5'%3e%3c/path%3e%3cpath%20d='M%20196.0%20119.0%20L%20118.0%20164.0'%3e%3c/path%3e%3cpath%20d='M%20144.0%20119.0%20L%20222.0%20164.0'%3e%3c/path%3e%3cpath%20d='M%20209.0%20126.5%20L%20131.0%20171.5'%3e%3c/path%3e%3cpath%20d='M%20131.0%20126.5%20L%20209.0%20171.5'%3e%3c/path%3e%3cpath%20d='M%20222.0%20134.0%20L%20144.0%20179.0'%3e%3c/path%3e%3cpath%20d='M%20118.0%20134.0%20L%20196.0%20179.0'%3e%3c/path%3e%3cpath%20d='M%20234.9%20141.5%20L%20157.0%20186.5'%3e%3c/path%3e%3cpath%20d='M%20105.0%20141.5%20L%20183.0%20186.5'%3e%3c/path%3e%3cpath%20d='M%20247.9%20149.0%20L%20170.0%20194.0'%3e%3c/path%3e%3cpath%20d='M%2092.1%20149.0%20L%20170.0%20194.0'%3e%3c/path%3e%3c/g%3e%3cg%20fill='none'%20stroke='%236898e2'%20stroke-width='1'%3e%3cpath%20d='M%20170.0%20119.0%20L%20170.0%2096.5'%3e%3c/path%3e%3ccircle%20cx='170.0'%20cy='96.5'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20201.2%20131.0%20L%20201.2%20111.5'%3e%3c/path%3e%3ccircle%20cx='201.2'%20cy='111.5'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20216.8%20152.0%20L%20216.8%20128.0'%3e%3c/path%3e%3ccircle%20cx='216.8'%20cy='128.0'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20138.8%20134.0%20L%20138.8%20113.0'%3e%3c/path%3e%3ccircle%20cx='138.8'%20cy='113.0'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20164.8%20143.0%20L%20164.8%20117.5'%3e%3c/path%3e%3ccircle%20cx='164.8'%20cy='117.5'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20185.6%20164.0%20L%20185.6%20144.5'%3e%3c/path%3e%3ccircle%20cx='185.6'%20cy='144.5'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20125.8%20153.5%20L%20125.8%20131.0'%3e%3c/path%3e%3ccircle%20cx='125.8'%20cy='131.0'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20157.0%20165.5%20L%20157.0%20144.5'%3e%3c/path%3e%3ccircle%20cx='157.0'%20cy='144.5'%20r='2.6'%3e%3c/circle%3e%3cpath%20d='M%20172.6%20183.5%20L%20172.6%20159.5'%3e%3c/path%3e%3ccircle%20cx='172.6'%20cy='159.5'%20r='2.6'%3e%3c/circle%3e%3c/g%3e%3cg%20fill='none'%20stroke='%239b6dff'%20stroke-width='1.1'%3e%3cpath%20d='M%20199.9%20149.8%20L%20199.9%20116.8'%20stroke-dasharray='3%203'%3e%3c/path%3e%3cpath%20d='M%20199.9%20112.8%20l%204%204%20l%20-4%204%20l%20-4%20-4%20Z'%3e%3c/path%3e%3ccircle%20cx='199.9'%20cy='149.8'%20r='7'%20stroke-dasharray='2%203'%20stroke-opacity='.55'%3e%3c/circle%3e%3cpath%20d='M%20132.3%20143.8%20L%20132.3%20112.3'%20stroke-dasharray='3%203'%3e%3c/path%3e%3cpath%20d='M%20132.3%20108.3%20l%204%204%20l%20-4%204%20l%20-4%20-4%20Z'%3e%3c/path%3e%3ccircle%20cx='132.3'%20cy='143.8'%20r='7'%20stroke-dasharray='2%203'%20stroke-opacity='.55'%3e%3c/circle%3e%3cpath%20d='M%20138.8%20168.5%20L%20138.8%20134.0'%20stroke-dasharray='3%203'%3e%3c/path%3e%3cpath%20d='M%20138.8%20130.0%20l%204%204%20l%20-4%204%20l%20-4%20-4%20Z'%3e%3c/path%3e%3ccircle%20cx='138.8'%20cy='168.5'%20r='7'%20stroke-dasharray='2%203'%20stroke-opacity='.55'%3e%3c/circle%3e%3c/g%3e%3cg%20style='animation:%20cfSweepX%207s%20cubic-bezier(.16,1,.3,1)%20infinite;'%3e%3cpath%20d='M%20170.0%2098.0%20L%2081.7%20149.0'%20stroke='%2375e7ff'%20stroke-width='1.4'%20style='filter:%20drop-shadow(0%200%208px%20rgba(117,231,255,.8));'%3e%3c/path%3e%3c/g%3e%3c/svg%3e)
See
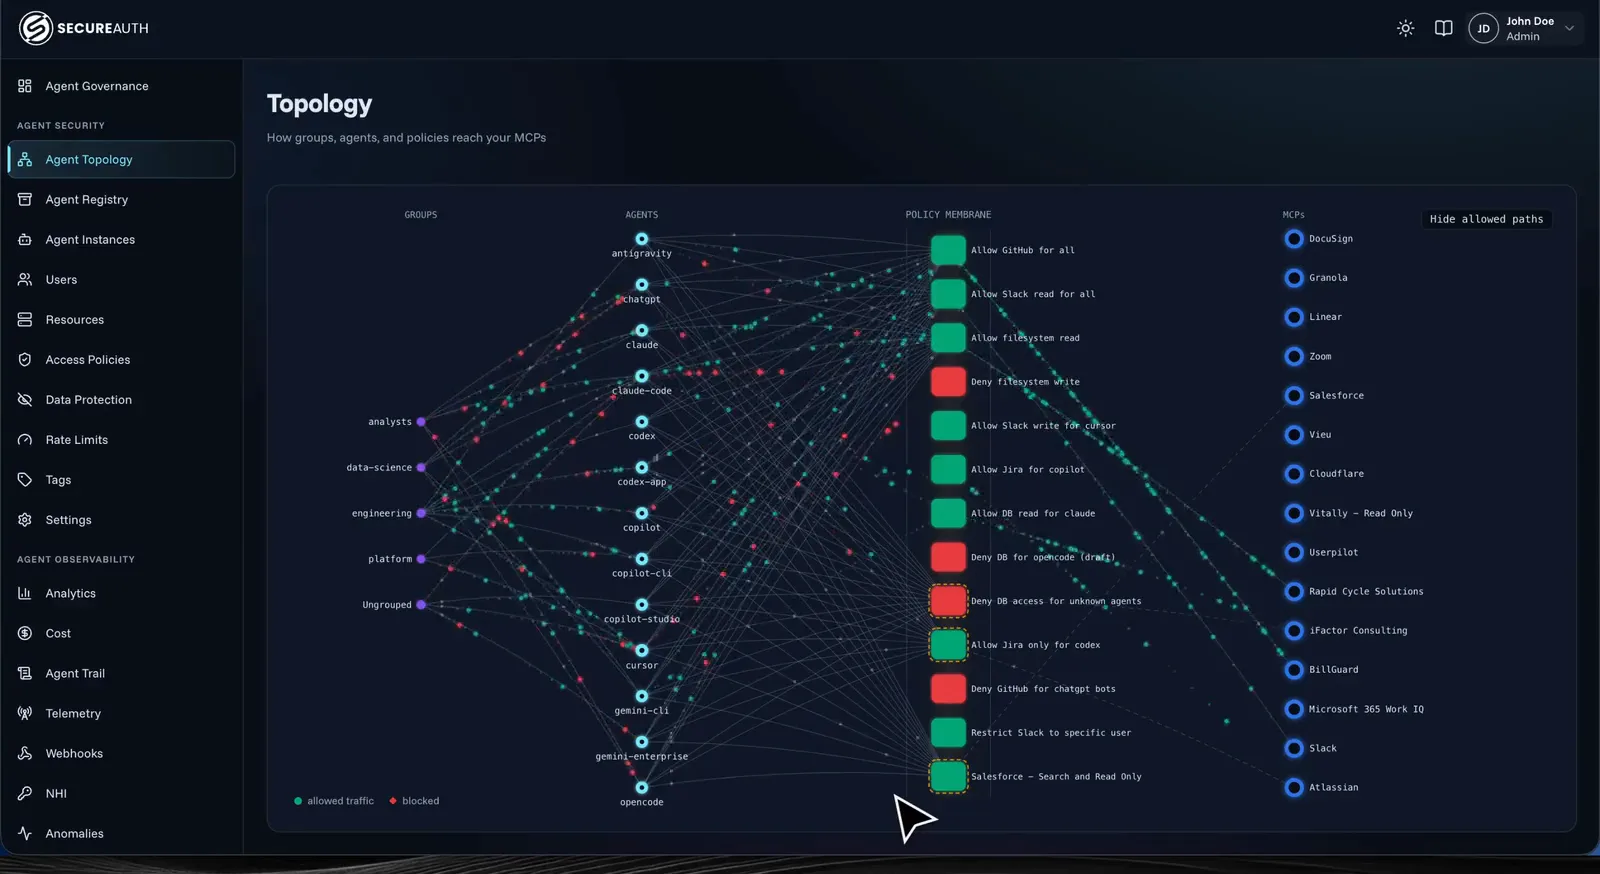
Every agent, service account, and instance in your systems, including unregistered ones.
Every non-human identity: agent, service account, instance.
The Observability layer
{.hiw-motion{display:none}}%3c/style%3e%3cdefs%3e%3clinearGradient%20id='hUnd'%20gradientUnits='userSpaceOnUse'%20x1='0'%20y1='34'%20x2='0'%20y2='174'%3e%3cstop%20offset='0%25'%20stop-color='%2375e7ff'%20stop-opacity='.55'%3e%3c/stop%3e%3cstop%20offset='58%25'%20stop-color='%236898e2'%20stop-opacity='.3'%3e%3c/stop%3e%3cstop%20offset='100%25'%20stop-color='%236898e2'%20stop-opacity='0'%3e%3c/stop%3e%3c/linearGradient%3e%3c/defs%3e%3cg%20fill='none'%20stroke='url(%23hUnd)'%20stroke-width='1'%3e%3cpath%20d='M%20170.0%2038.0%20L%20242.7%2080.0%20L%20170.0%20122.0%20L%2097.3%2080.0%20Z'%3e%3c/path%3e%3cpath%20d='M%20170.0%2083.0%20L%20224.6%20114.5%20L%20170.0%20146.0%20L%20115.4%20114.5%20Z'%3e%3c/path%3e%3cpath%20d='M%20170.0%20128.0%20L%20206.4%20149.0%20L%20170.0%20170.0%20L%20133.6%20149.0%20Z'%3e%3c/path%3e%3c/g%3e%3cg%20fill='none'%20stroke='%236898e2'%20stroke-width='1'%20stroke-opacity='.7'%3e%3cpath%20d='M%20170.0%2080.0%20L%20170.0%20149.0'%3e%3c/path%3e%3c/g%3e%3cg%20fill='none'%20stroke='%2375e7ff'%20stroke-width='1.2'%3e%3ccircle%20cx='170.0'%20cy='80.0'%20r='4.4'%3e%3c/circle%3e%3ccircle%20cx='170.0'%20cy='114.5'%20r='3.4'%3e%3c/circle%3e%3ccircle%20cx='170.0'%20cy='149.0'%20r='2.6'%3e%3c/circle%3e%3c/g%3e%3ccircle%20class='hiw-motion'%20r='2.6'%20fill='%2375e7ff'%20style='filter:%20drop-shadow(0%200%207px%20rgba(117,231,255,.95));'%3e%3canimateMotion%20dur='5.5s'%20repeatCount='indefinite'%20calcMode='spline'%20keySplines='0.16%201%200.3%201'%20keyTimes='0;1'%20keyPoints='0;1'%20path='M%20170.0%2080.0%20L%20170.0%20149.0'%3e%3c/animateMotion%3e%3c/circle%3e%3c/svg%3e)
Understand
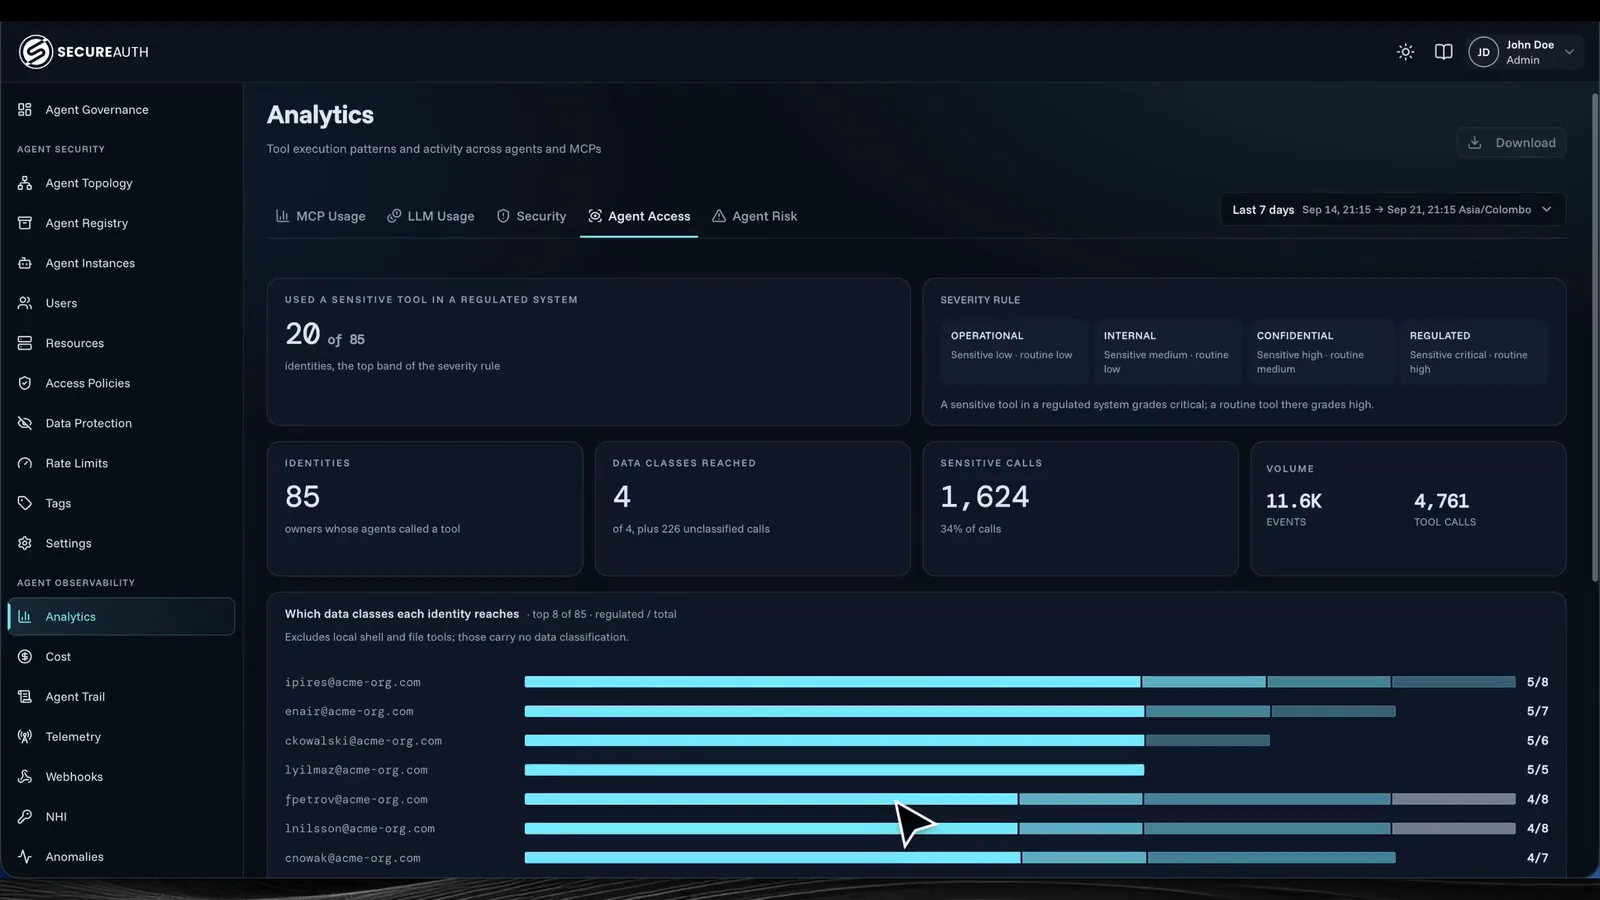
Every delegation chain, showing who authorized each agent, and a trail of autonomous access to corporate data.
Behavioral baselines for every action, reach, and cost.
The decision layer
'%20stroke-width='1'%3e%3cpath%20d='M%20216.8%20140.0%20L%20123.2%20194.0%20L%20123.2%20125.0%20L%20216.8%2071.0%20Z'%3e%3c/path%3e%3cpath%20d='M%20193.4%20153.5%20L%20193.4%2084.5'%20stroke-opacity='.5'%3e%3c/path%3e%3cpath%20d='M%20162.2%20171.5%20L%20162.2%20102.5'%20stroke-opacity='.5'%3e%3c/path%3e%3cpath%20d='M%20138.8%20185.0%20L%20138.8%20116.0'%20stroke-opacity='.5'%3e%3c/path%3e%3c/g%3e%3cg%20fill='none'%20stroke='%236898e2'%20stroke-width='1'%3e%3cpath%20d='M%20150.5%2073.3%20L%20197.3%20100.3'%3e%3c/path%3e%3cpath%20d='M%2096.0%20104.8%20L%20142.7%20131.8'%3e%3c/path%3e%3c/g%3e%3cg%20fill='none'%20stroke='%2375e7ff'%20stroke-width='1.3'%3e%3cpath%20d='M%20197.3%20100.3%20L%20244.0%20127.3'%3e%3c/path%3e%3cpath%20d='M%20142.7%20131.8%20L%20189.5%20158.8'%3e%3c/path%3e%3ccircle%20cx='244.0'%20cy='127.3'%20r='2.8'%3e%3c/circle%3e%3ccircle%20cx='189.5'%20cy='158.8'%20r='2.8'%3e%3c/circle%3e%3c/g%3e%3cg%20fill='none'%20stroke='%23f24b6b'%20stroke-width='1.2'%3e%3cpath%20d='M%20123.2%20105.5%20L%20170.0%20132.5'%20stroke-dasharray='4%203'%3e%3c/path%3e%3cpath%20d='M%20166.0%20128.5%20l%208%208%20M%20174.0%20128.5%20l%20-8%208'%20stroke-linecap='round'%3e%3c/path%3e%3c/g%3e%3cpath%20d='M%20216.8%2071.0%20L%20123.2%20125.0'%20fill='none'%20stroke='%2375e7ff'%20stroke-width='1.4'%20stroke-opacity='.8'%20style='filter:%20drop-shadow(0%200%209px%20rgba(117,231,255,.65));'%3e%3c/path%3e%3c/svg%3e)
Control
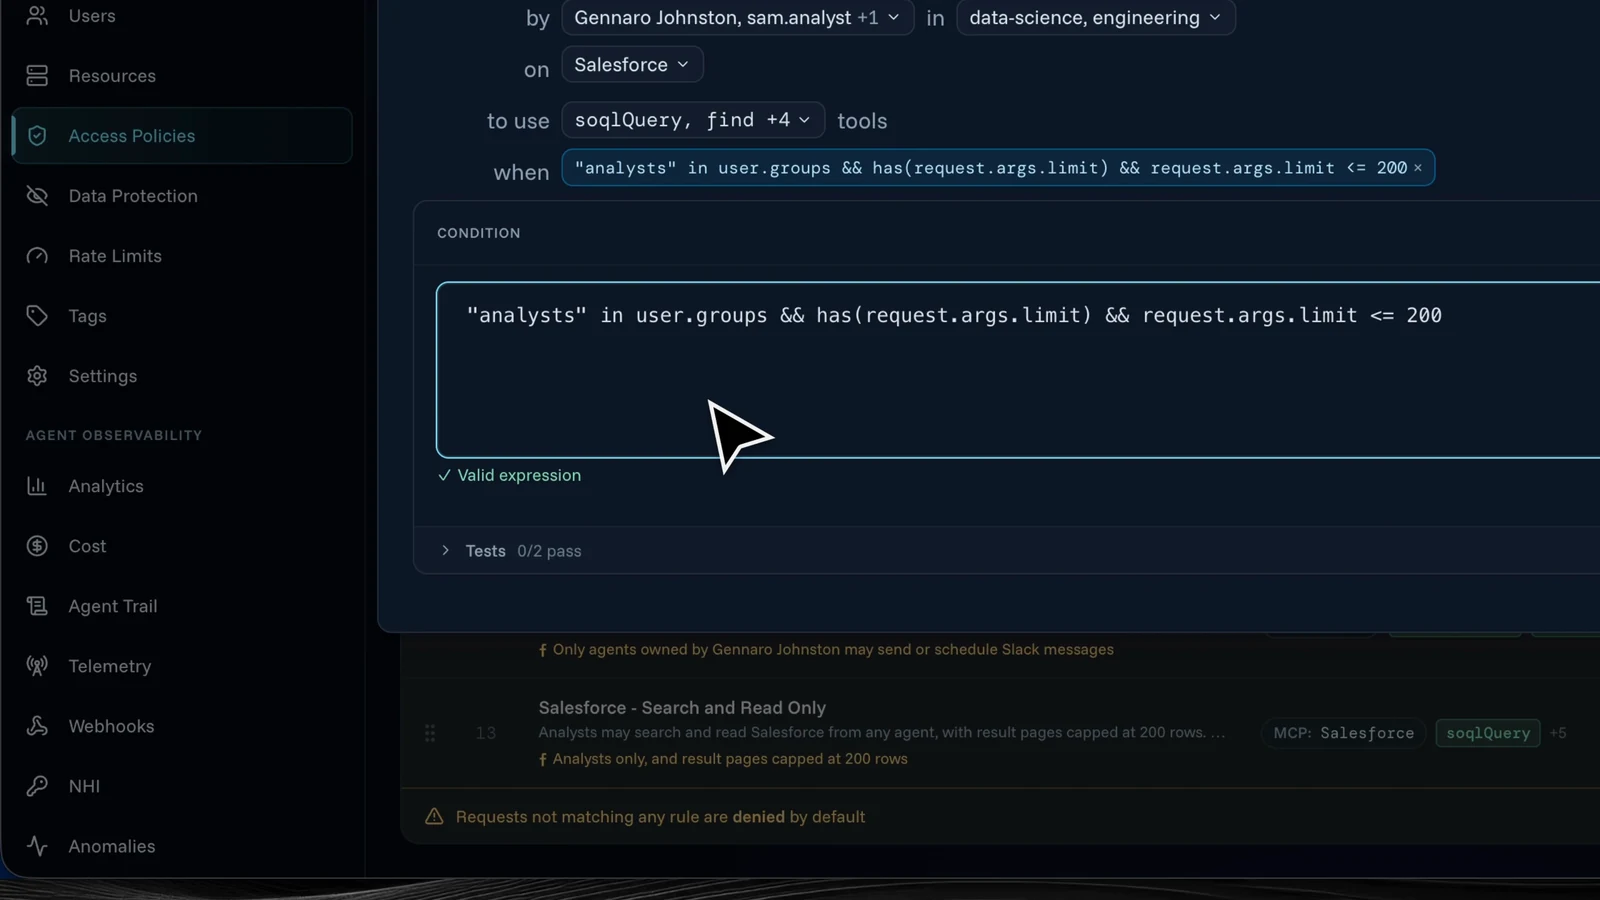
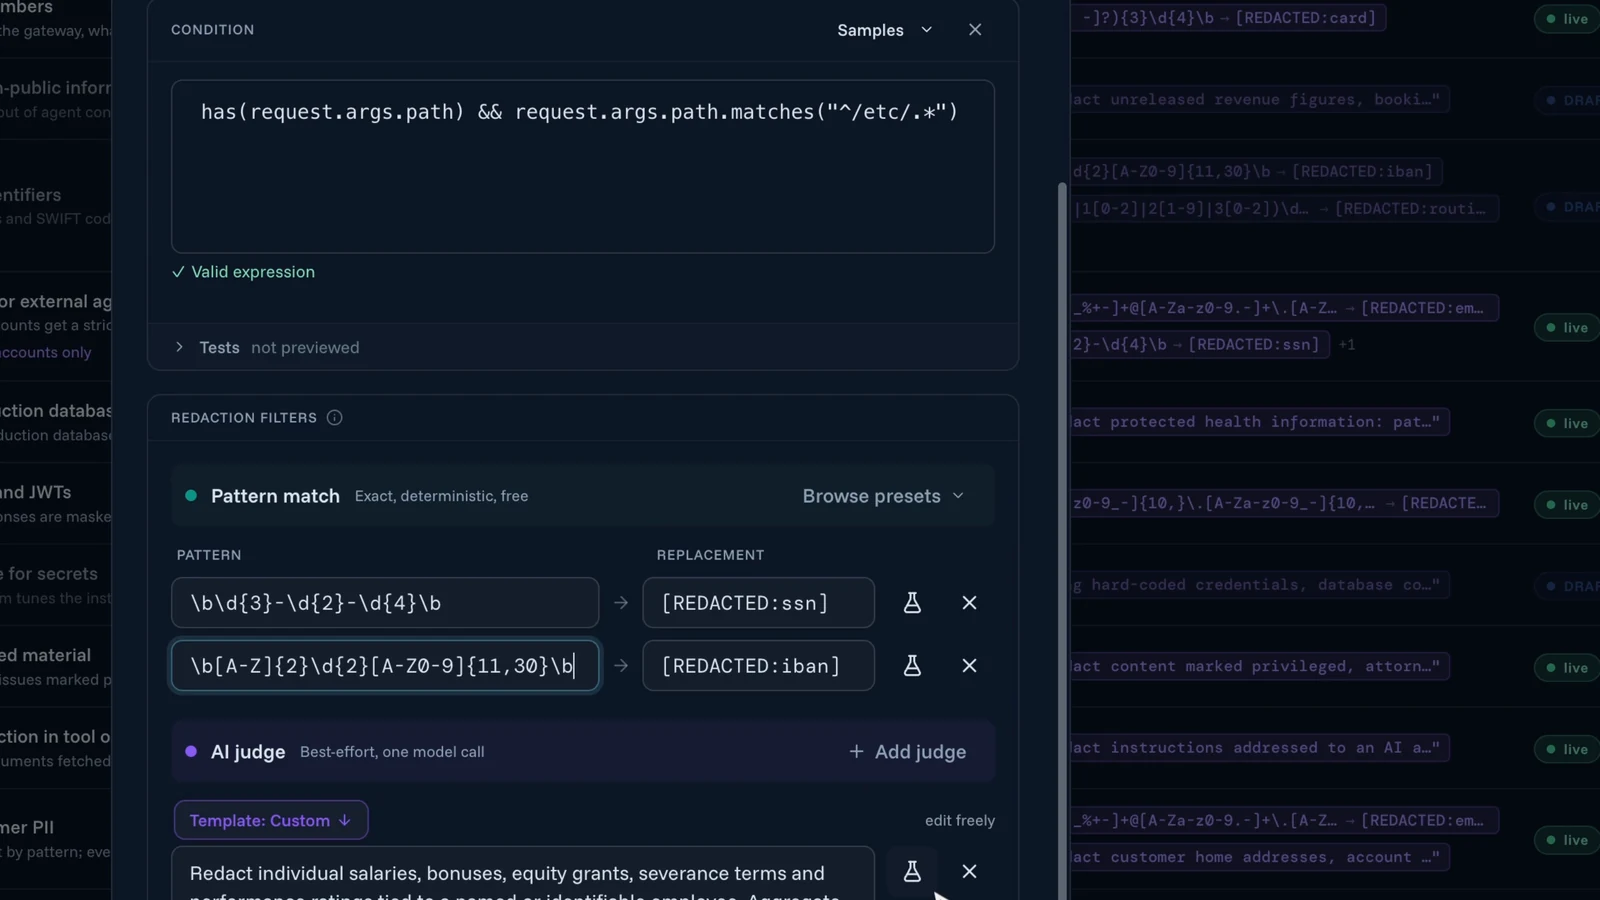
Every action agents take, decided in real time before they can do anything.
One decision per action, in milliseconds.